Medical committee: permits and credentialing · In development
SIMKOMED
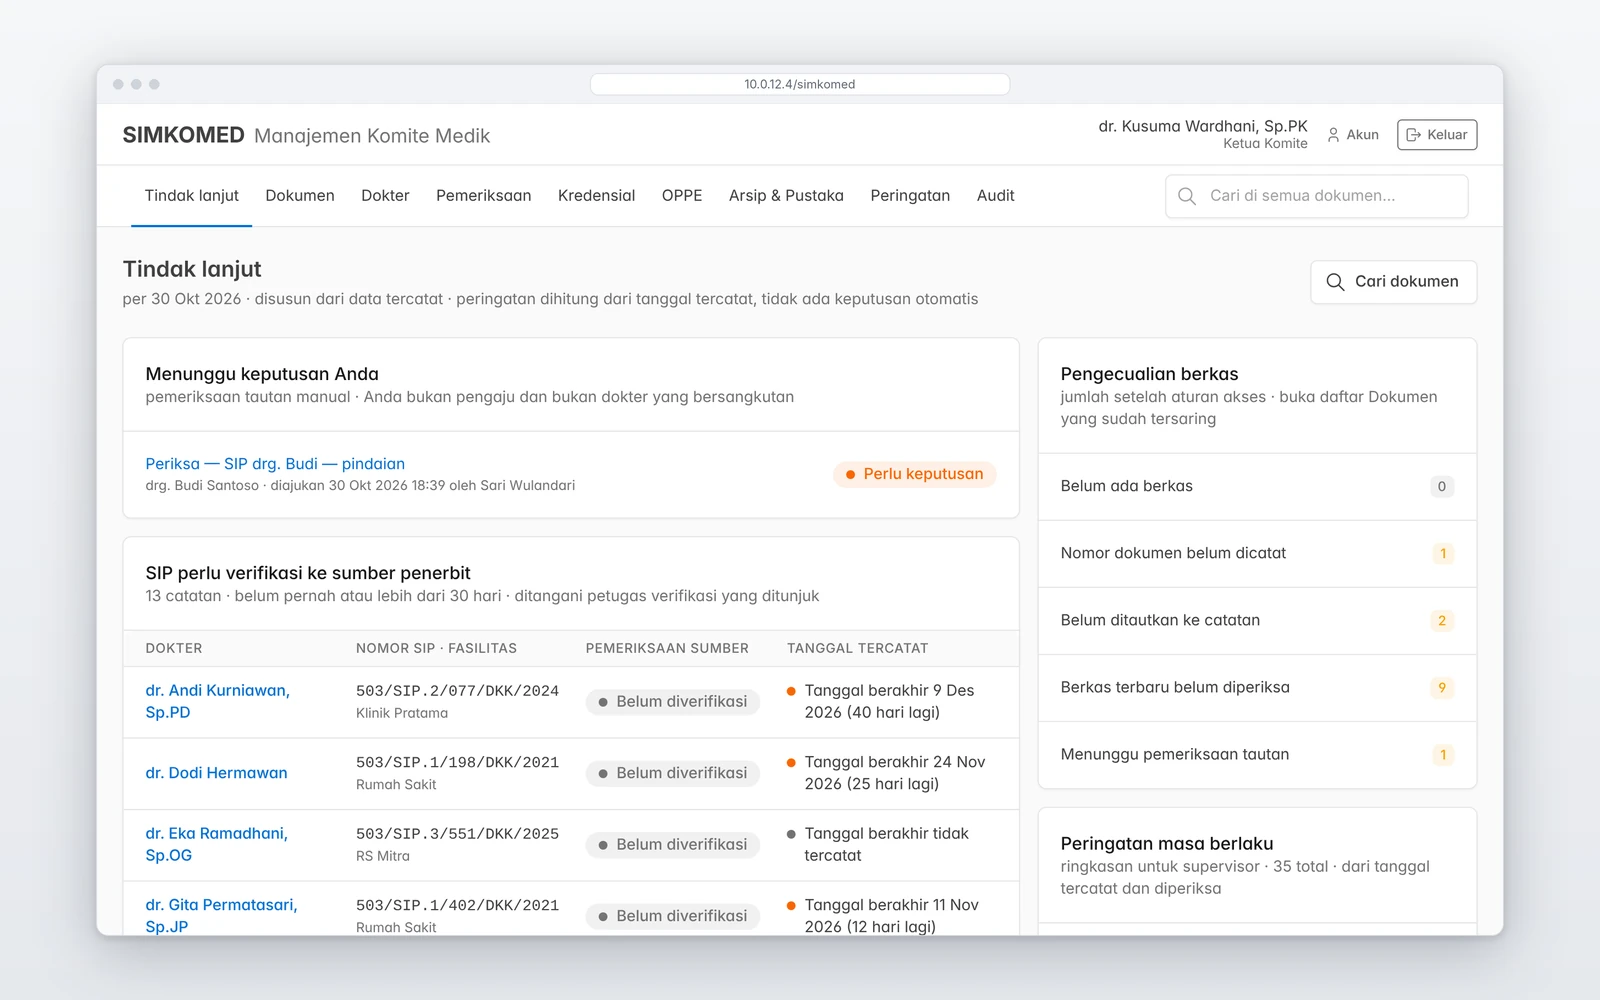
Doctors' permits, credentialing and OPPE evaluations for a hospital's medical committee, with the rules enforced in the database.
Problem
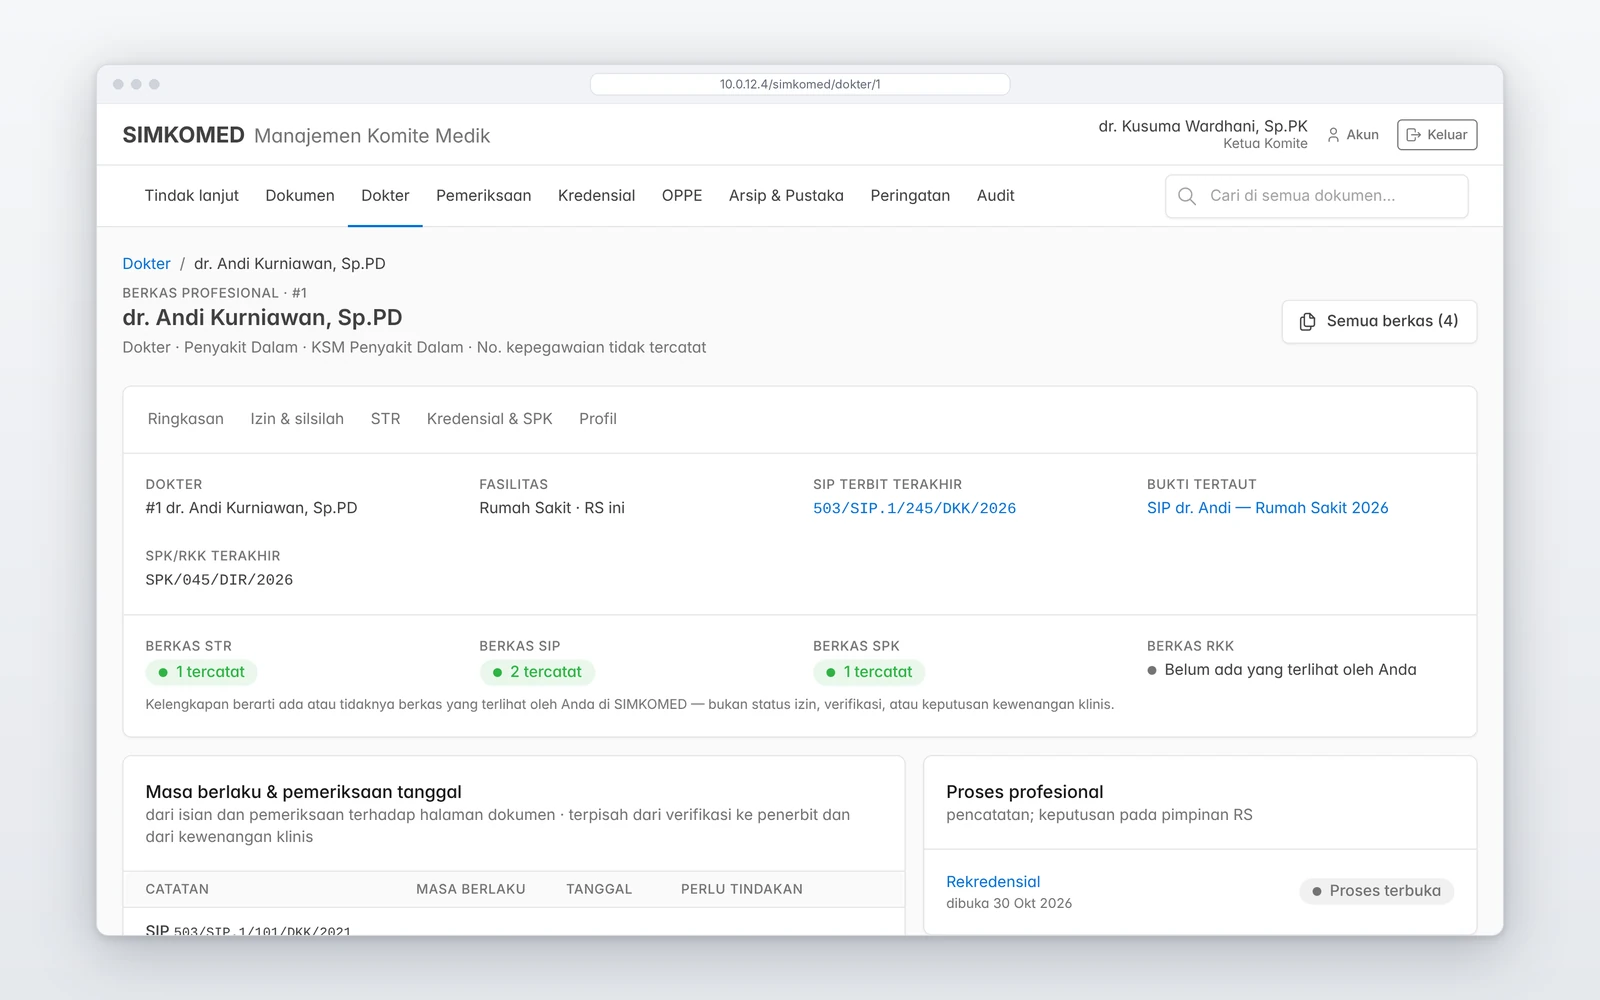
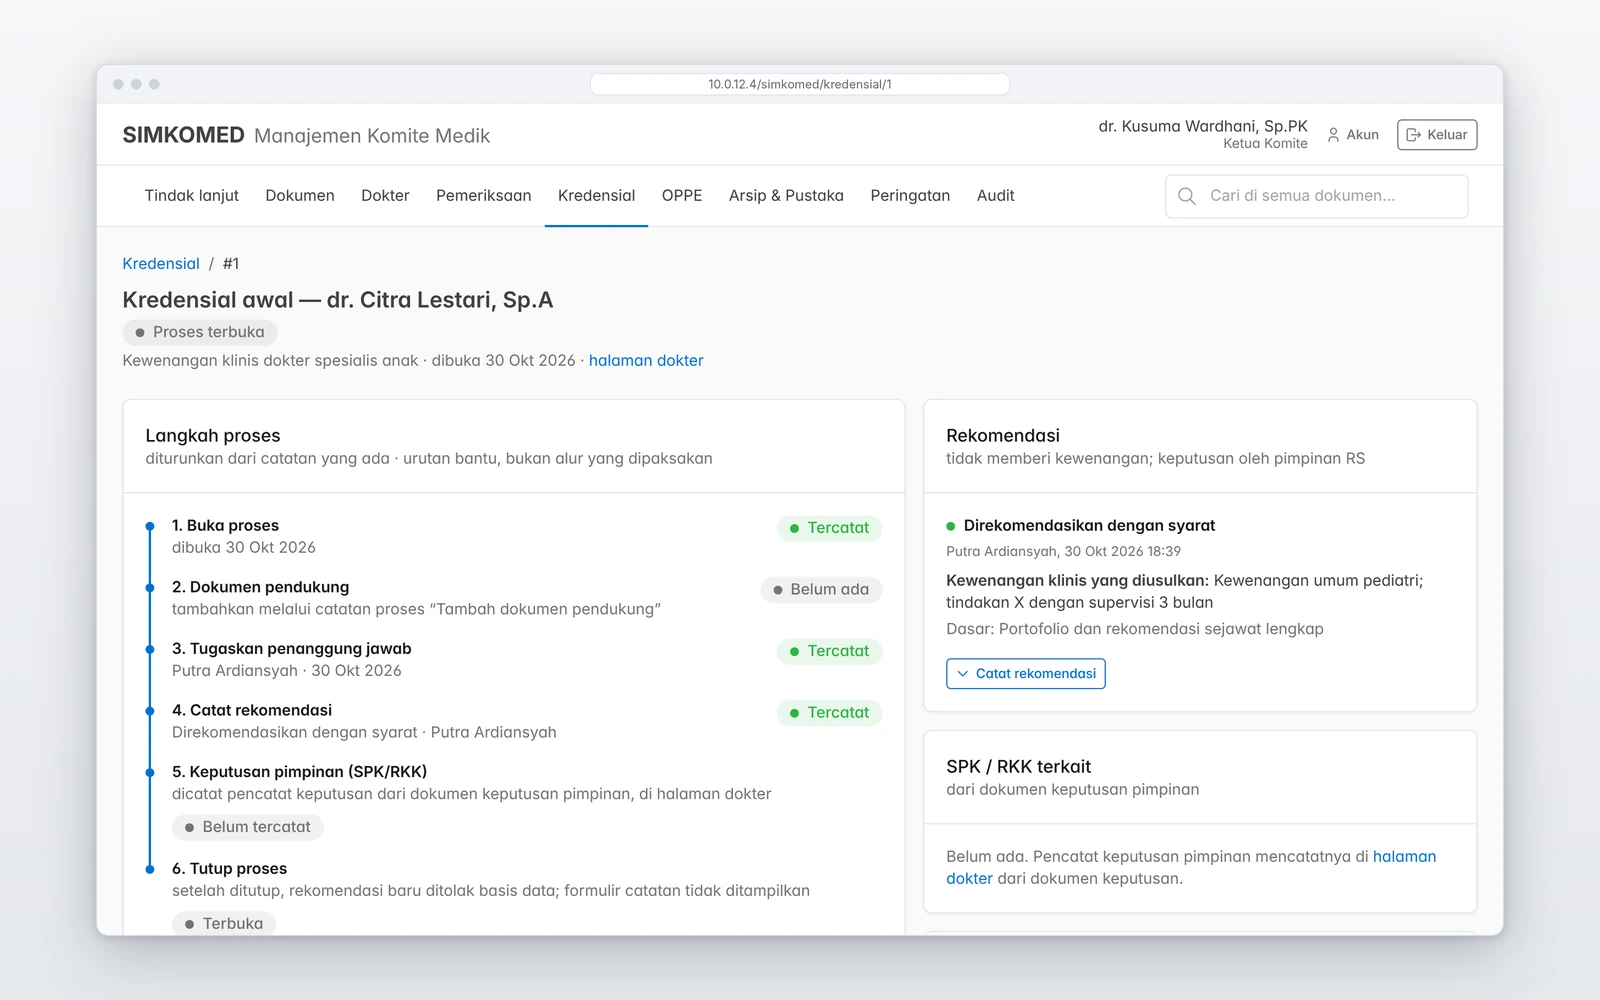
A medical committee works from documents: permits with validity dates, credentialing decisions and evaluations, handled by people with different duties. The record has to show who verified or decided what, and stop anyone acting on their own file.
What I built
A server-rendered Starlette application on PostgreSQL. Every request binds the signed-in user in the database, and triggers and row-level security enforce separation of duties.
Key screens
On a phone
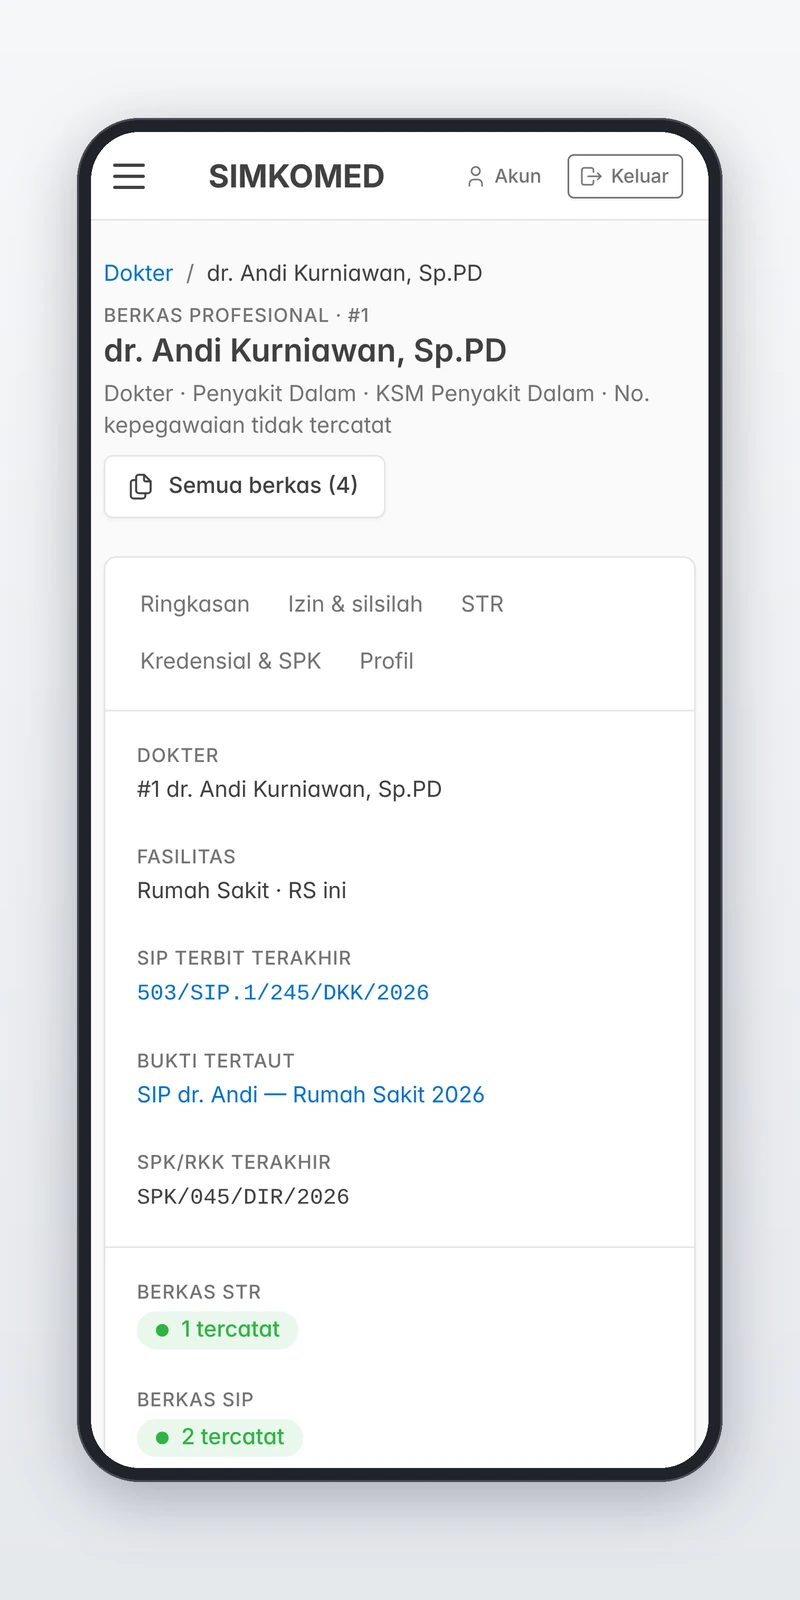
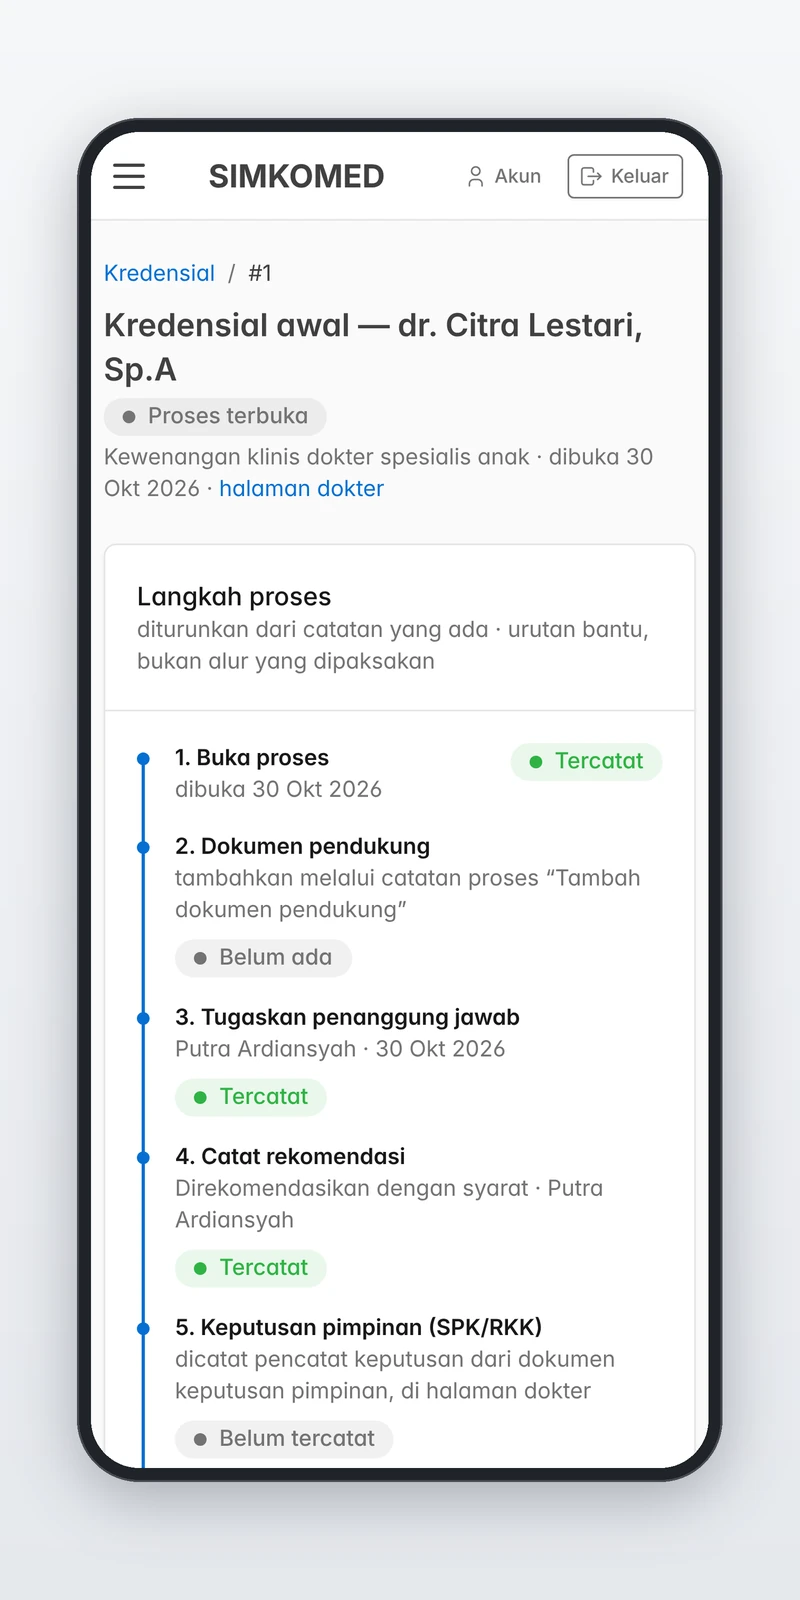
See all screens (7)
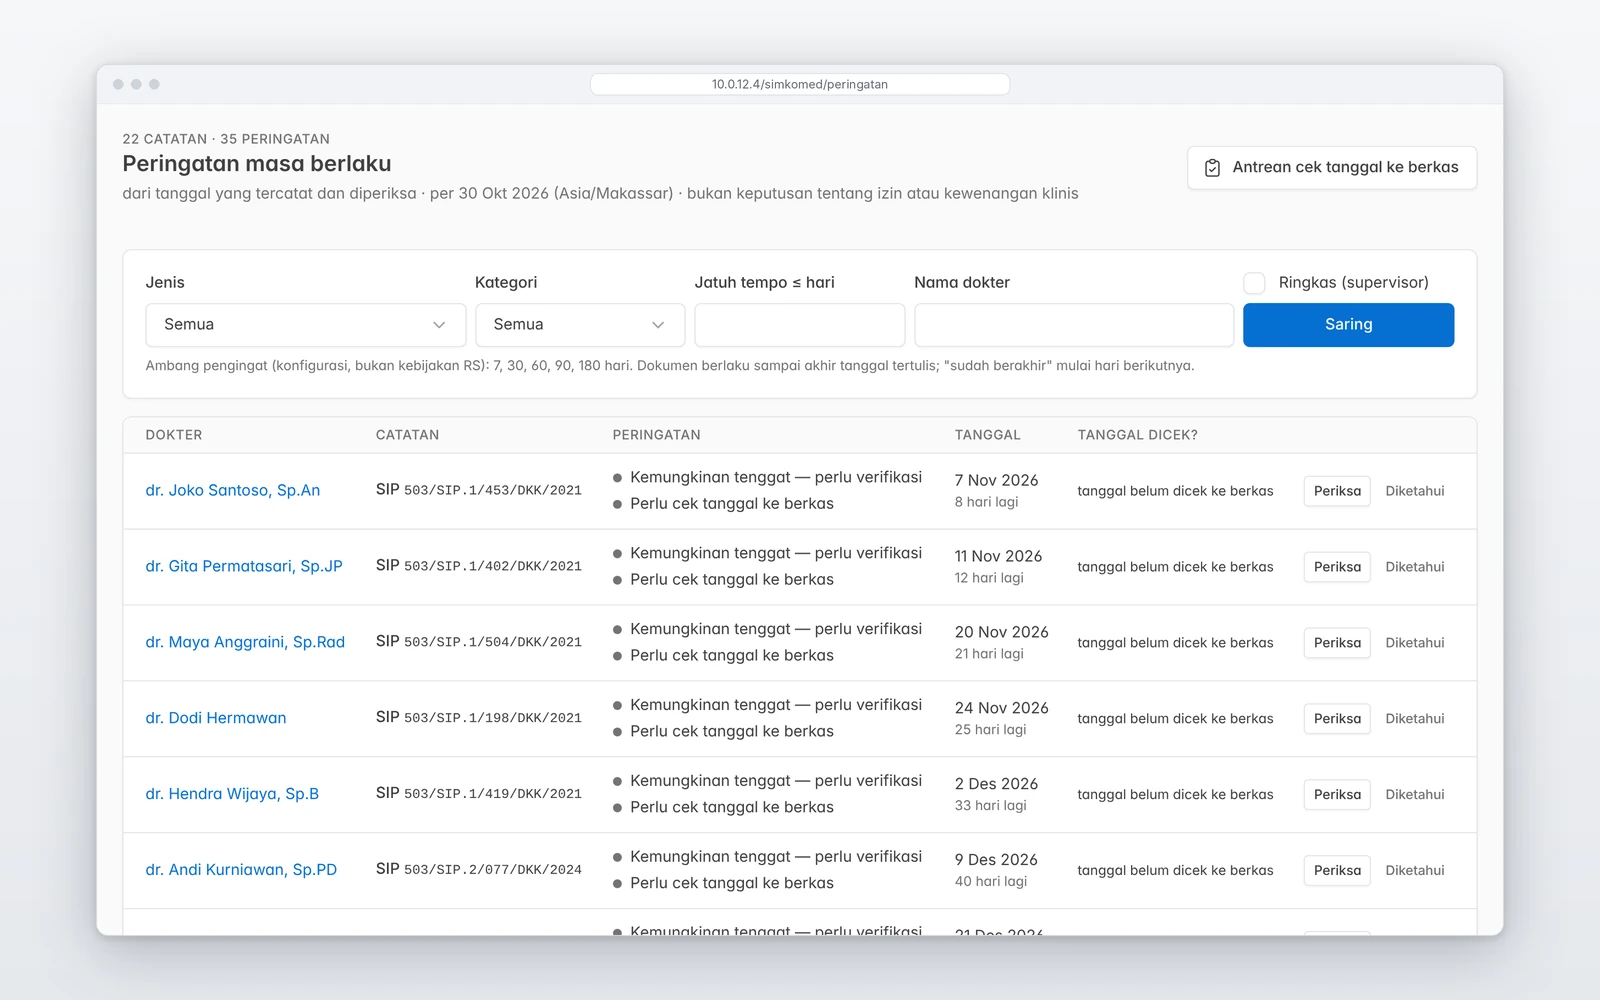
All names, numbers and files in these screens are invented.
My role
Built the local v1: schema and migrations, the security model, the web app, and the test and browser end-to-end suites.
Key decisions
- Separation of duties is a database rule.
- A requester can't review their own request, and a reviewer linked to a doctor can't act on that doctor's records.
- Restricted means restricted everywhere.
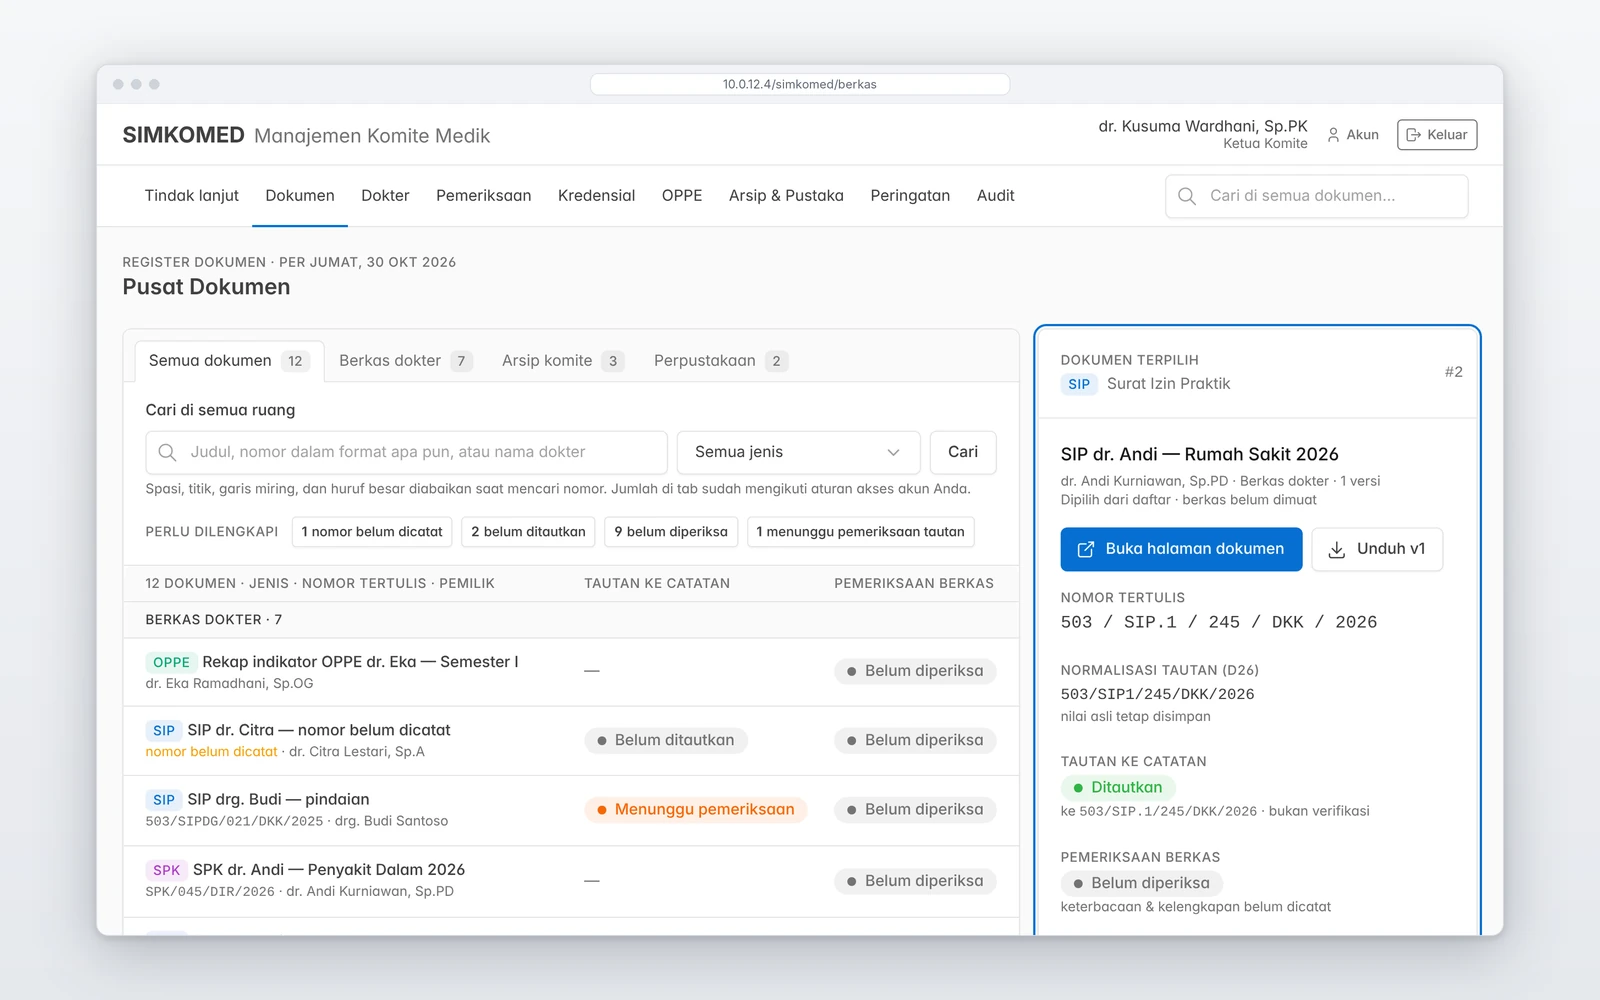
- Row-level security covers lists, search, counts, links, preview and download.
- Nothing is overwritten.
- History is append-only and a new file version never replaces an old one.
Stack
Python 3.13StarletteJinja2PostgreSQLRow-level securityWebAuthn passkeyspytestPlaywright
Status
- Status
- Local v1 candidate: not deployed, sample data only
- Not in v1 yet
- Production hosting, TLS, SSO and MFA, notifications, exports